 Mostafa Ashraf

Description.
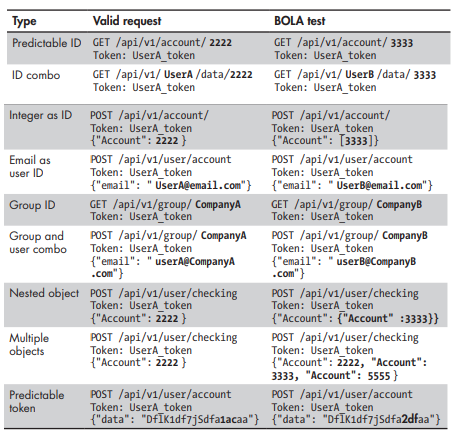
Broken Object Level Authorization (BOLA): security vulnerability that occurs when authorization controls are lacking or missing, UserA will be able to request UserB’s (along with many other) resources
Key Aspects of BOLA:
- Resource ID: The resource identifier specifies a unique resource (e.g., number)
- Requests that access resources.
you will need to know the requests that are necessary to obtain resources that your account should not be authorized to access. - Missing or flawed access controls.
Absence of proper access controls, allowing unauthorized access to resources
Authorization Testing Strategy
When searching for authorization vulnerabilities the most effective way to find authorization weaknesses is to create two accounts and perform A-B testing. The A-B testing process consists of:
- Create a UserA account.
- Use the API and discover requests that involve resource IDs as UserA.
- Document requests that include resource IDs and should require authorization.
- Create a UserB account.
- Obtaining a valid UserB token and attempt to access UserA’s resources
Checklist
—