 Mostafa Ashraf

XSS via Malicious PDF in Document Share Feature Leading to Session Token Exfiltration
Hello, In this writeup I’m going to talk about a Cross-Site Scripting (XSS) vulnerability I found in the document sharing feature of a cobrowse platform, the platform allows a support agent to create a live session with a client to help fix issues, and the client can share a PDF if the agent asks for it.
Target
let’s call our target example.com, a cobrowse platform used to create live support sessions between an agent and a client.
Discovery
i was testing the document sharing feature during an active cobrowse session, and i noticed the app renders shared PDF content without any sanitization
so i thought, what if the PDF itself contains embedded JavaScript?
Attack Scenario
- I Started the session as a support agent
- in a second browser, i joind as client
- once the session is active, locate and click the Share Document button on the visitor side
- craft a malicious PDF file with an embedded JavaScript XSS payload, using PDF JavaScript actions
- upload and share the crafted PDF through the document share feature
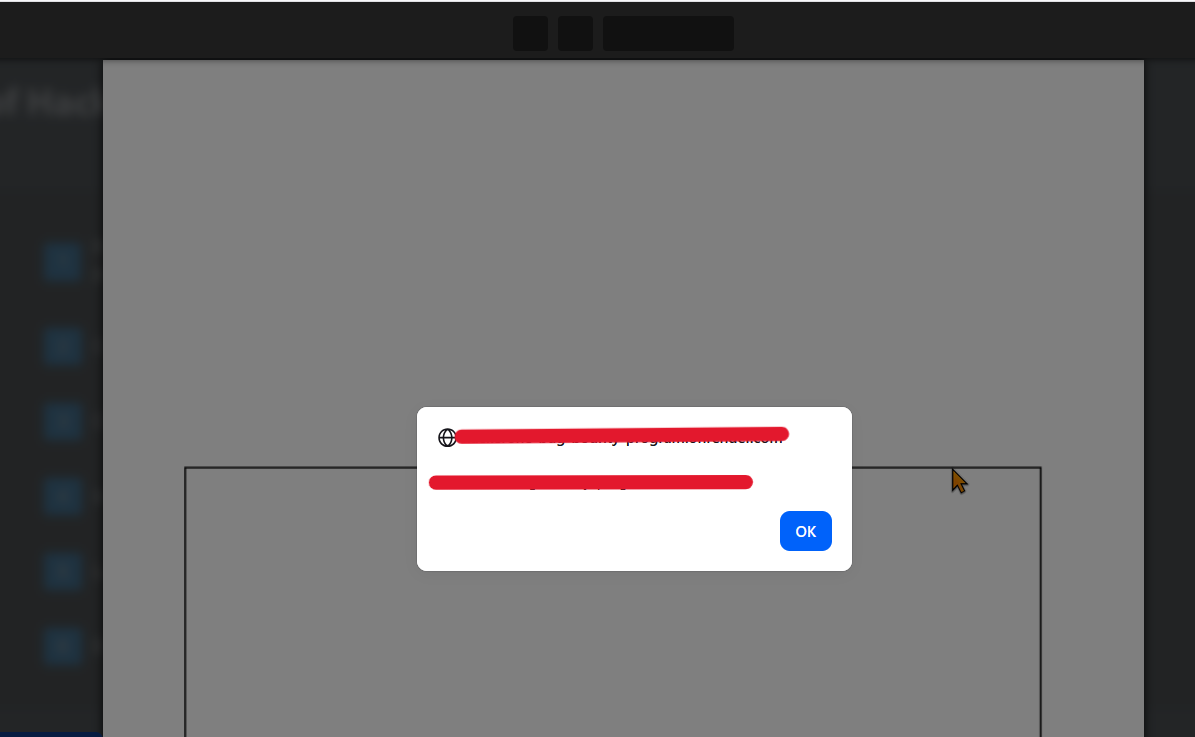
- the JavaScript payload executes in the browser context of
example.com - the alert dialog reveals the full domain, confirming code execution in the app’s origin
Escalation
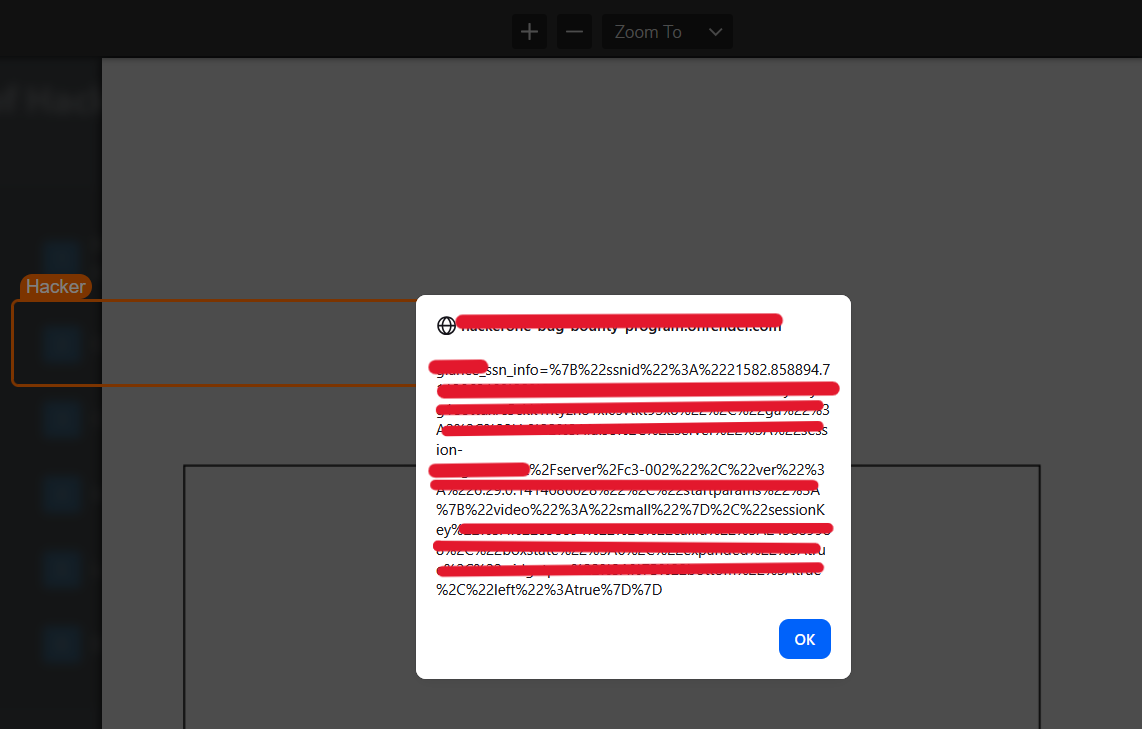
i didn’t stop at a simple proof-of-concept alert, i wanted to push it further to demonstrate real impact
so i escalated the payload to dump the example_ssn_info object, which contains:
- a live session token
- the session ID
- session server routing info
- call metadata
this means the payload can fully exfiltrate a live session token, which enables session hijacking
Impact
- an attacker can share a malicious PDF during a live cobrowse session to execute arbitrary JavaScript in the victim’s browser context
- the payload can read and exfiltrate the
example_ssn_infoobject, exposing the live session token, session ID, and routing/call metadata - with the exfiltrated session token, an attacker could potentially hijack an active cobrowse session, impersonating either the agent or the client
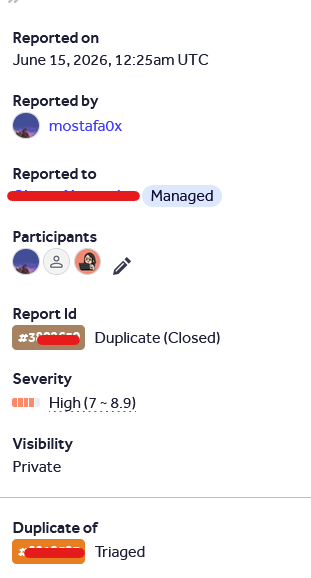
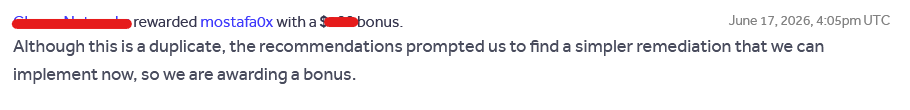
Unfortunately, this report was marked as a duplicate, but the program was incredibly generous. They found my recommendations valuable and rewarded me with a bonus.
have a nice day , see you Soon