 Mostafa Ashraf

Description
bepractical.tech. It’s a platform that offers various challenges and labs for cybersecurity enthusiasts and bug hunters to practice their skills. The site provides hands-on experience with real-world scenarios, allowing users to test and improve their abilities in finding and exploiting vulnerabilities.
—
Login
First we will login with the credentials given
john@bepractical.tech:john@123
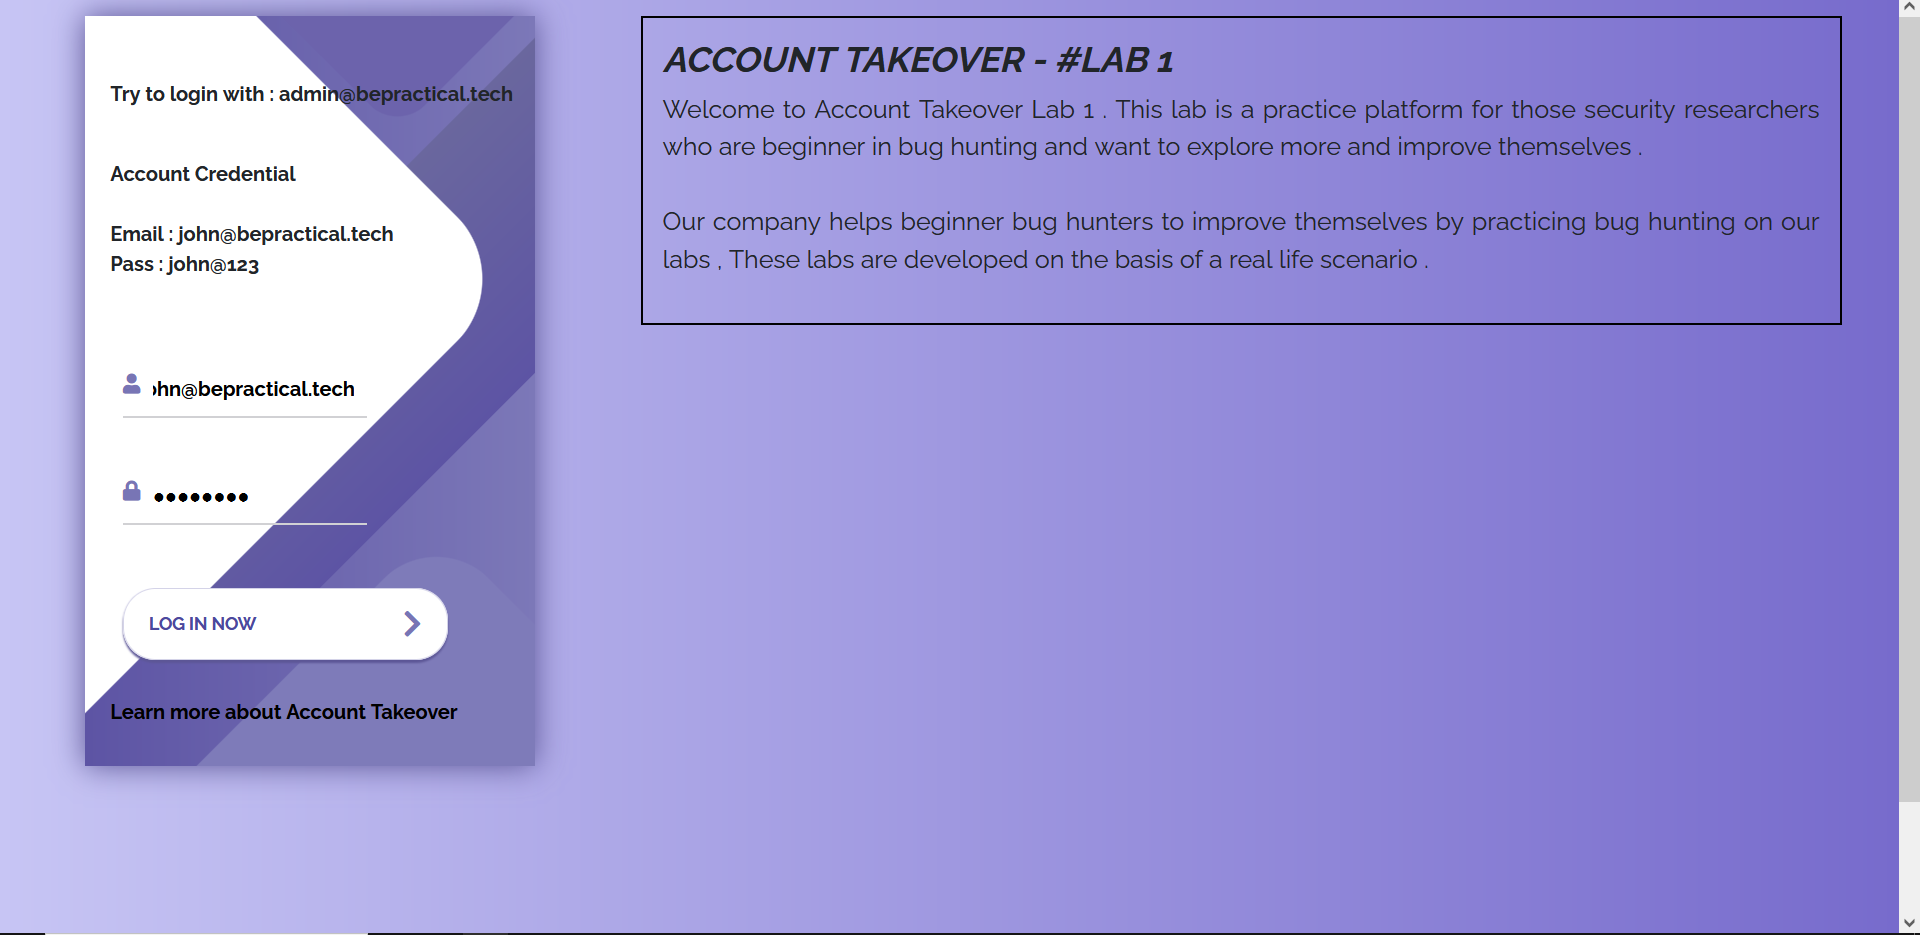
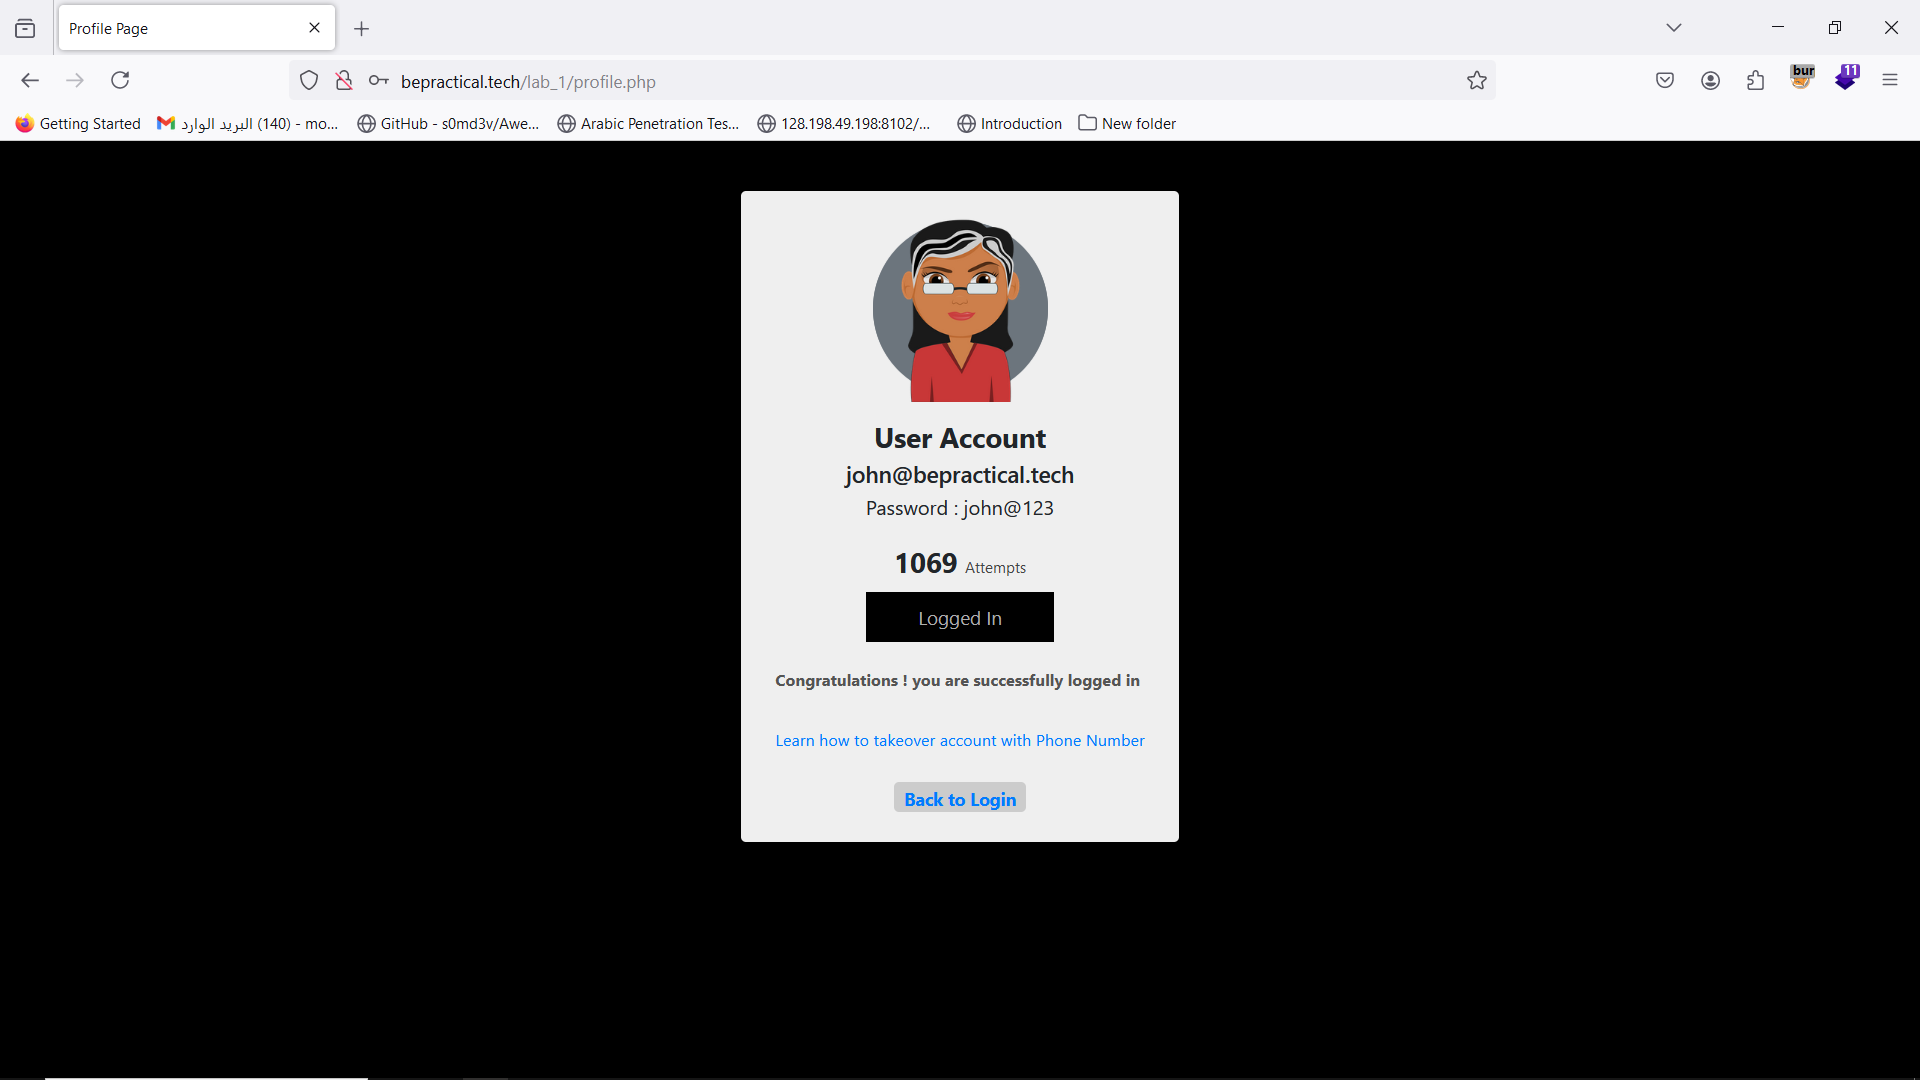
As you can see, we were logged in as John.
Now, let’s go back to the login page, intercept the same request with BurpSuite, and send it to the Repeater.
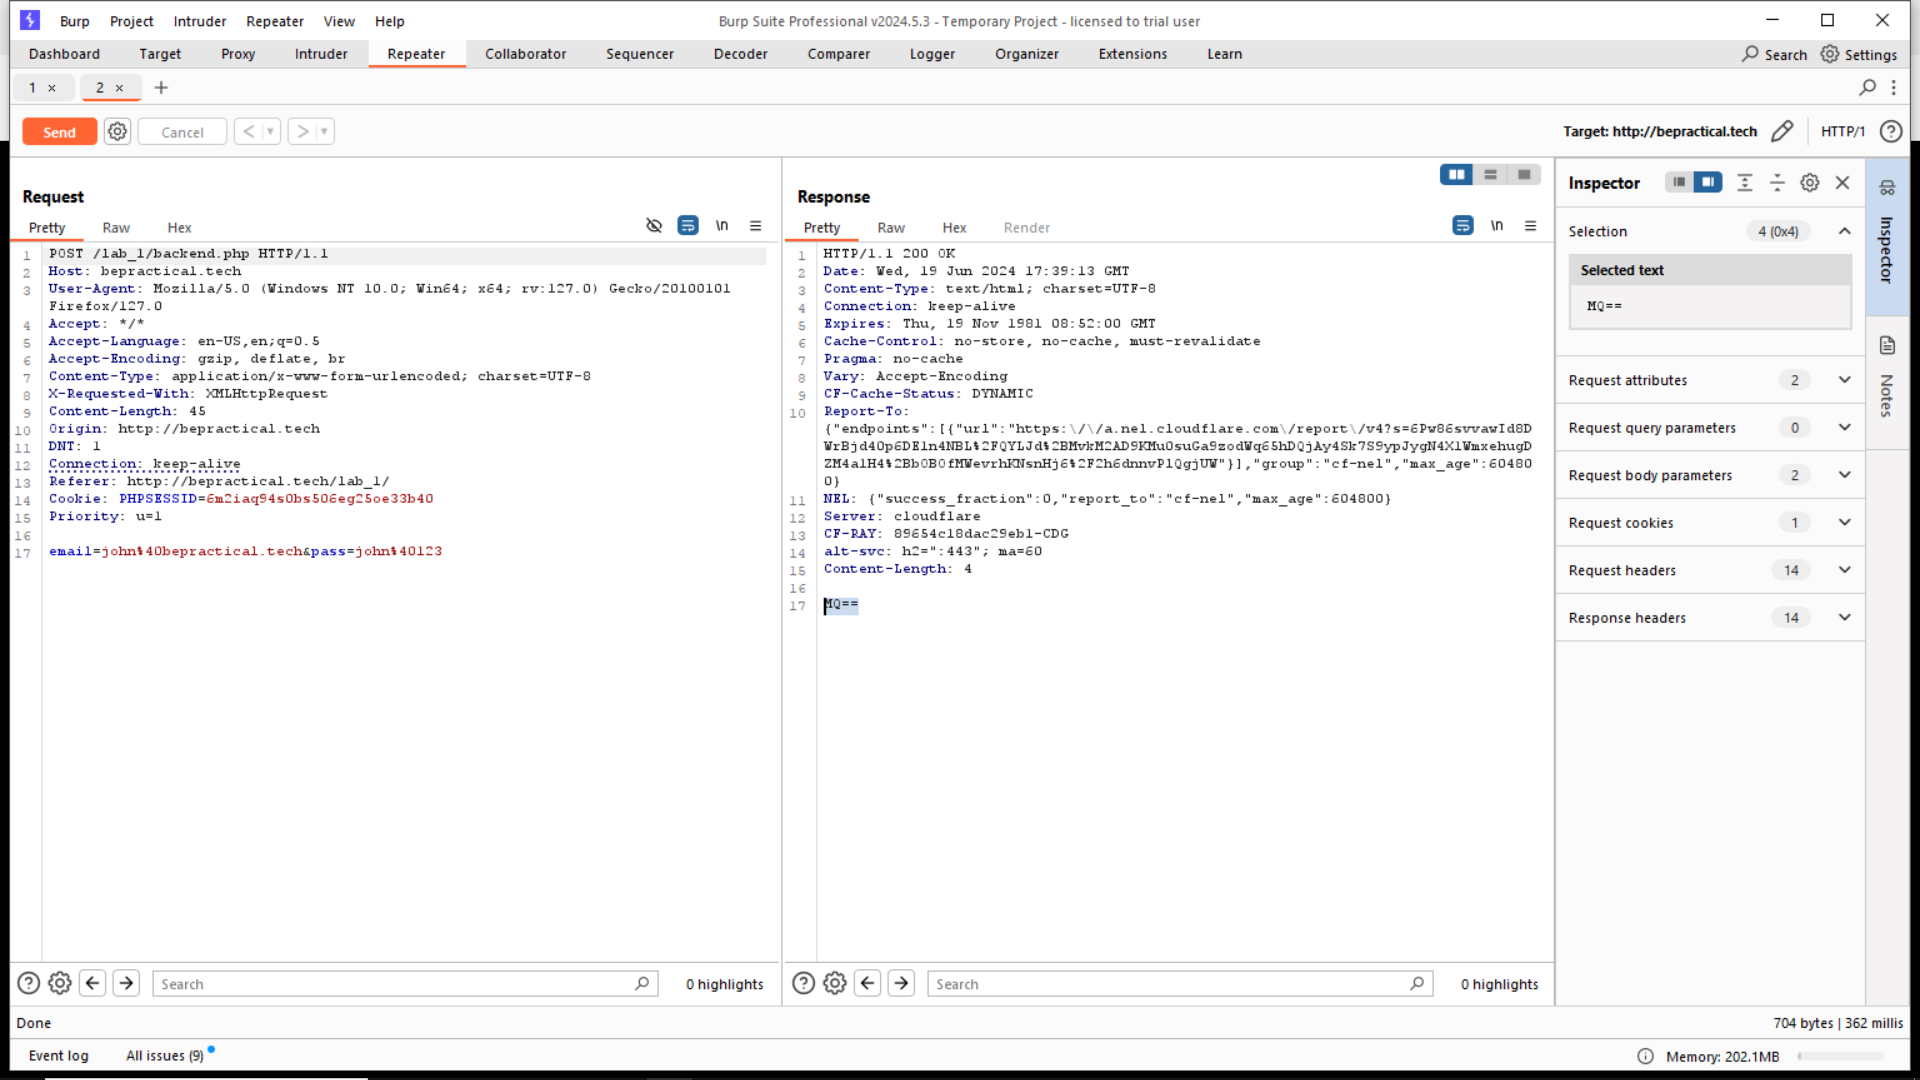
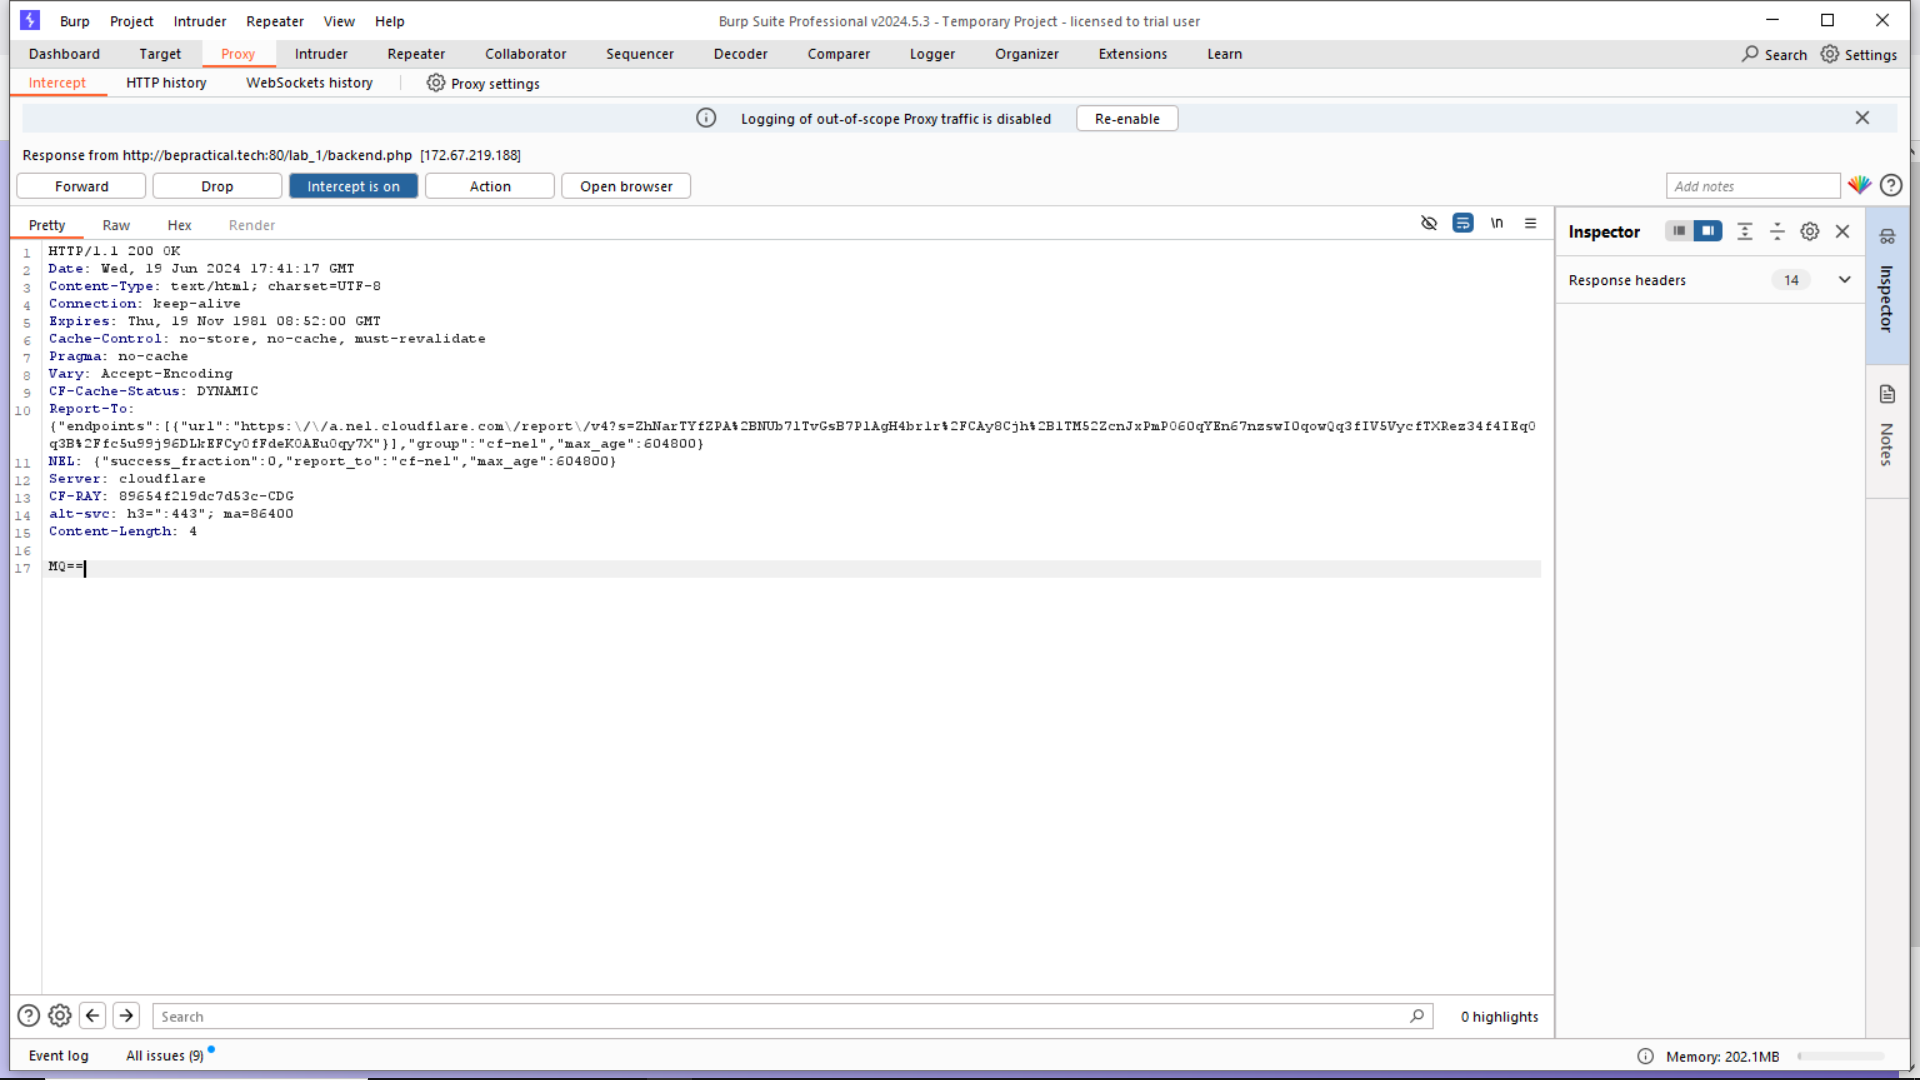
When we logged in with the given credentials, the response was MQ==, which is Base64 for 1.
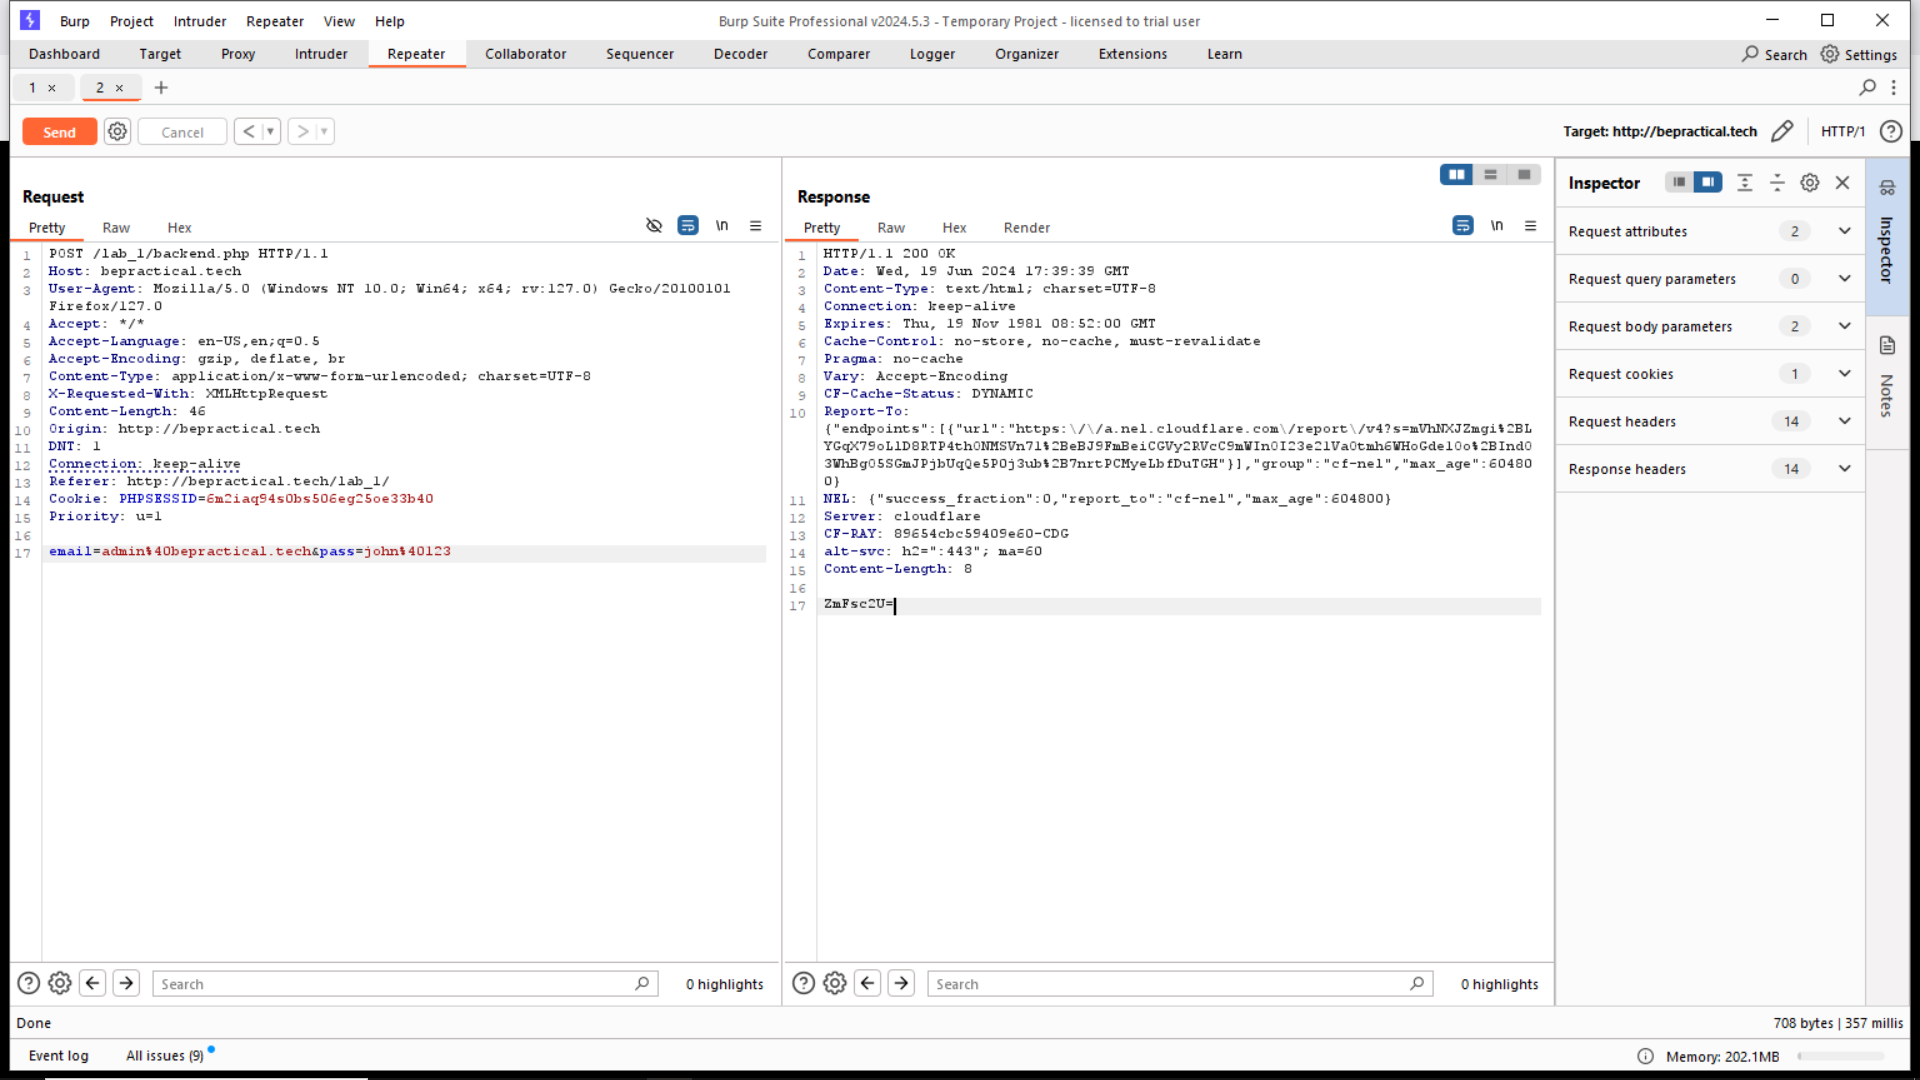
If we change the email parameter to admin@bepractical.tech, the response will be ZmFsc2U=, which means false.
Response Manipulation
Immediately, I thought about response manipulation.
So, I went back and intercepted the request. I changed the email to admin@bepractical.tech, right-clicked, selected Do intercept, chose response to this request, and then forwarded it. After that, I changed ZmFsc2U= to MQ== and forwarded the request again
Now, turn intercept off, then go back to Firefox.
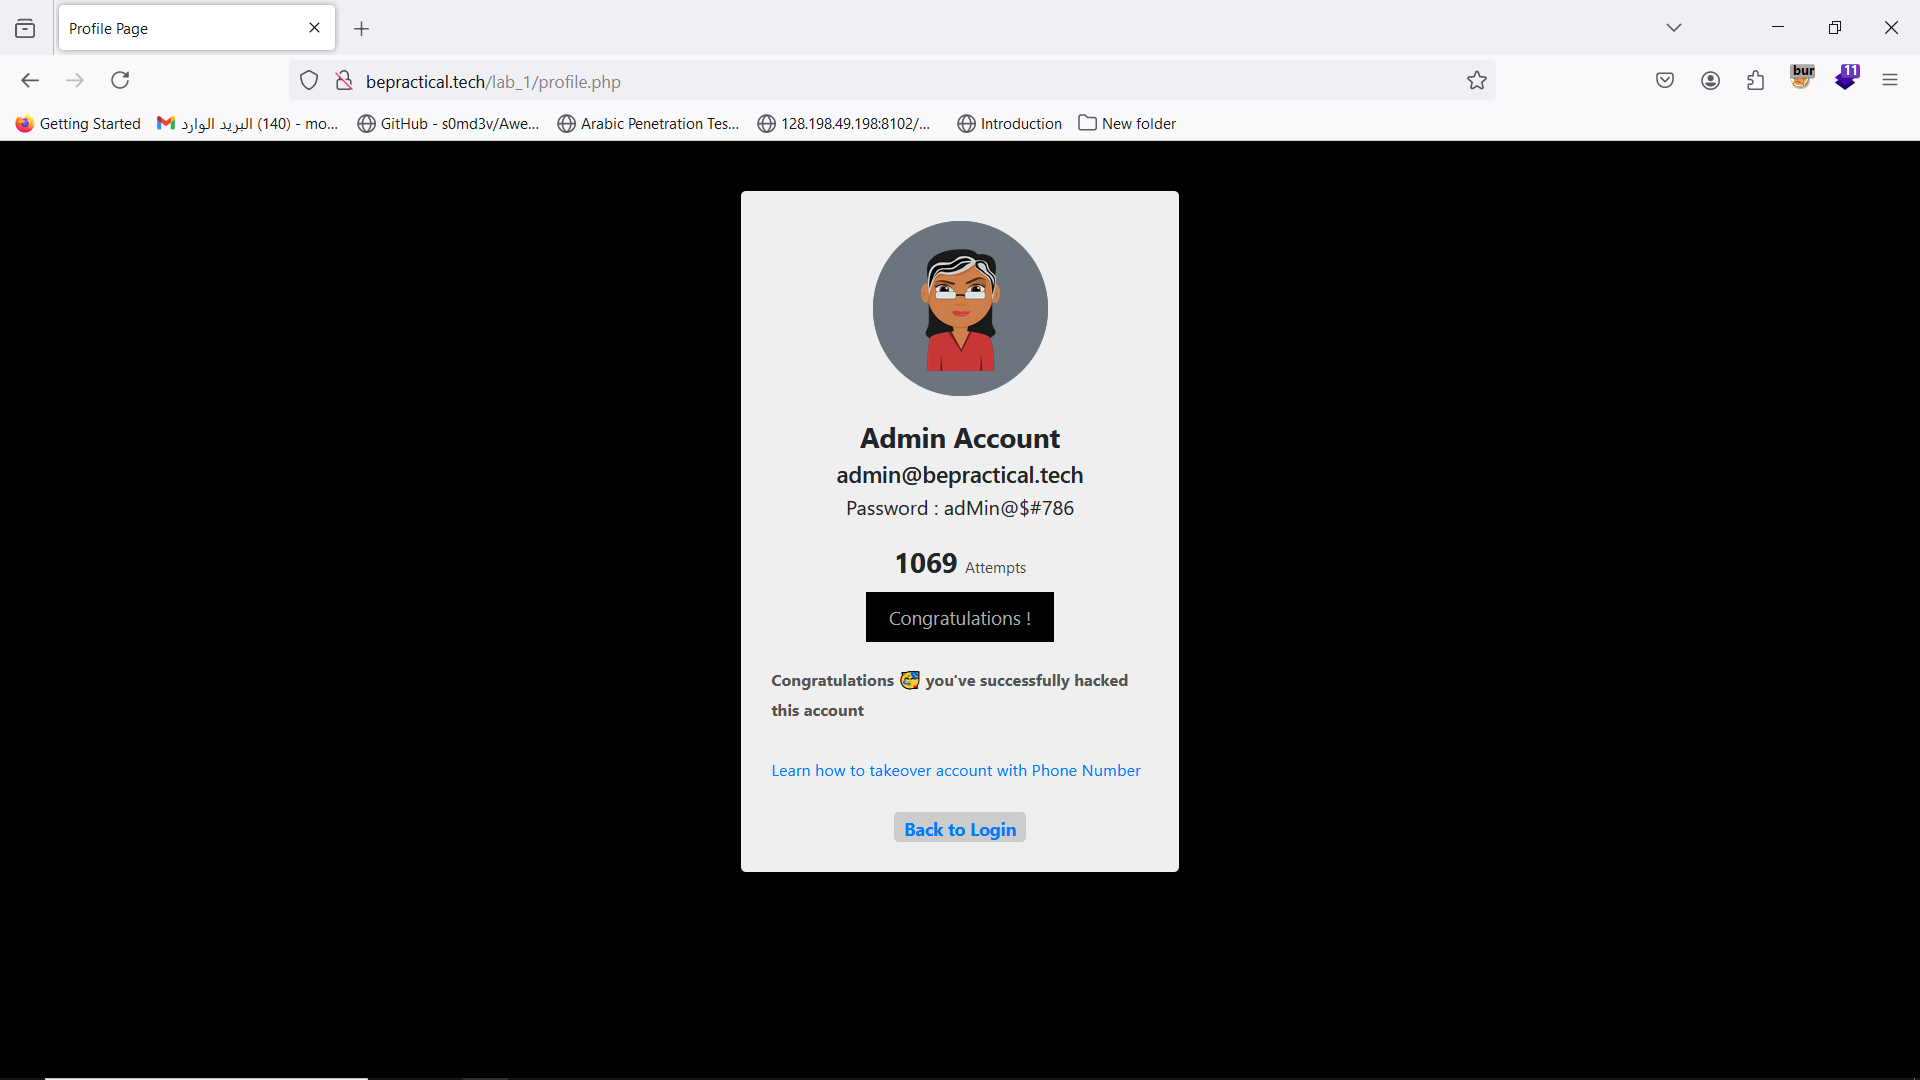
GG lab is solved.